Memory-Safe Languages: 5 Common Misunderstandings Debunked
Memory safety eliminates buffer overflows but introduces new complexity in dependency management and runtime behavior that requires distinct operational oversight.
Memory-safe languages prevent specific memory corruption errors like buffer overflows, but they do not eliminate all vulnerabilities. Developers must still address logic flaws, dependency risks, and configuration errors. Security teams should treat these languages as one layer of defense, not a total solution for application security.
Misreading: Memory safety equals complete security
Correct reading: Memory safety specifically prevents invalid memory access operations. It stops buffer overflows, use-after-free errors, and null pointer dereferences. It does not prevent SQL injection, command injection, or broken access control. A developer can write memory-safe code that still allows an attacker to read sensitive data through logic flaws. You must still validate inputs and enforce authorization. Relying solely on memory safety leaves the application exposed to non-memory vulnerabilities.
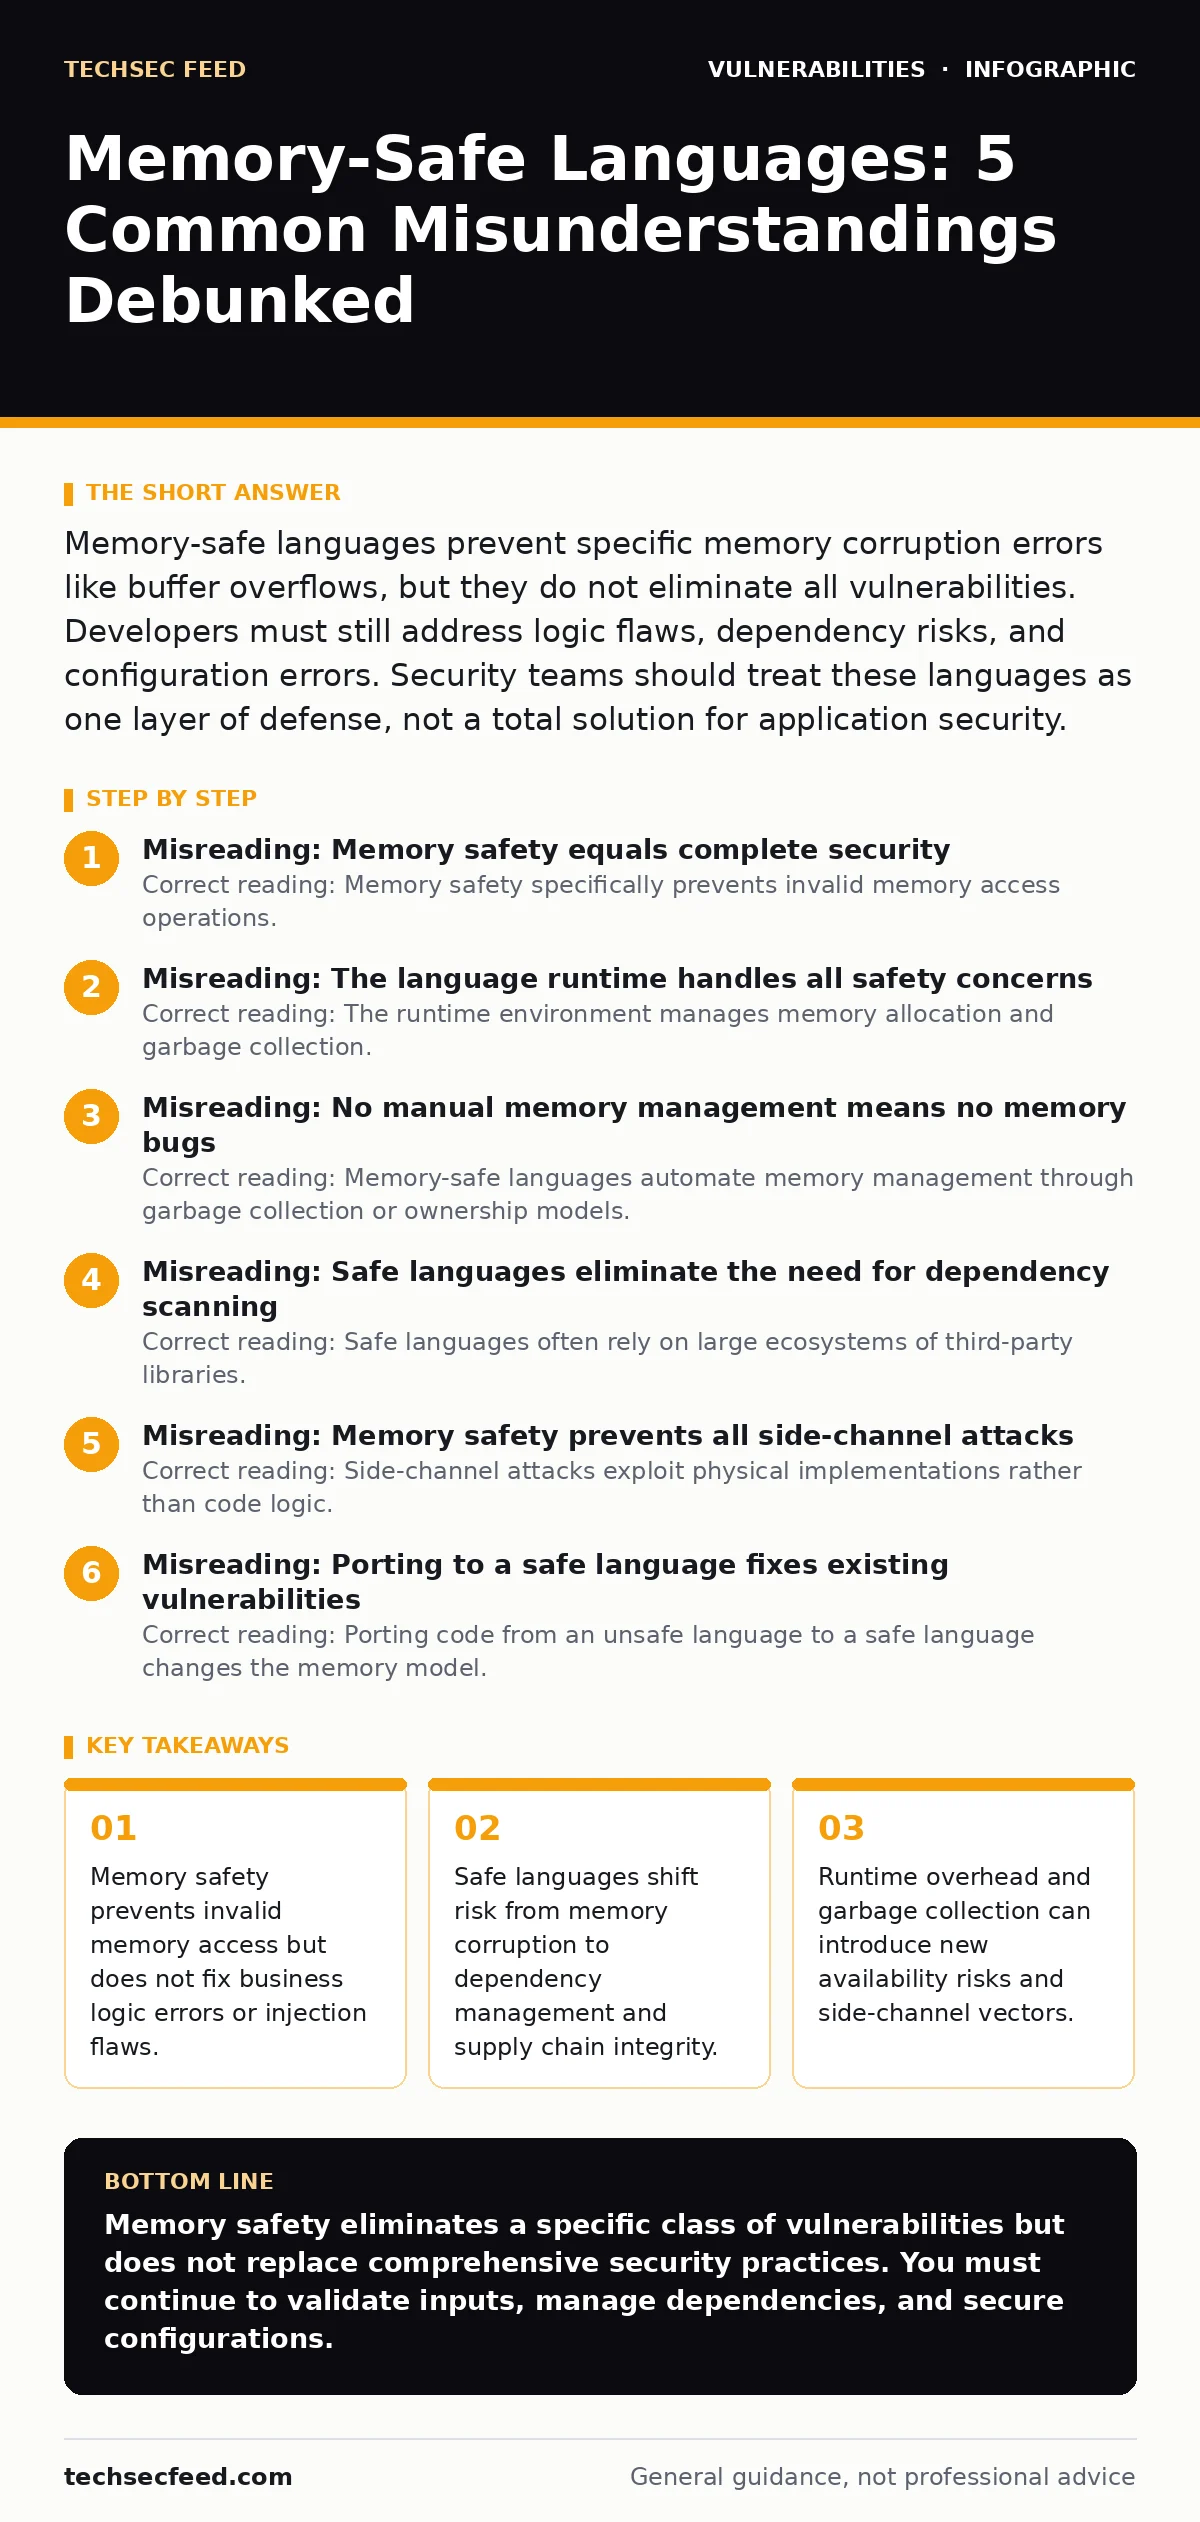
Misreading: The language runtime handles all safety concerns
Correct reading: The runtime environment manages memory allocation and garbage collection. It does not manage security policies or input validation. The runtime introduces its own attack surface. If the runtime contains a vulnerability, every application using it is at risk. You must monitor the runtime for updates separately from your application code. A secure application built on a compromised runtime remains vulnerable. Treat the runtime as a critical dependency.
Misreading: No manual memory management means no memory bugs
Correct reading: Memory-safe languages automate memory management through garbage collection or ownership models. This eliminates manual allocation errors. It does not eliminate logical errors in how memory is used. Developers can still create memory leaks by holding references too long. They can create integer overflow vulnerabilities when calculating buffer sizes. They can create race conditions in concurrent code. These bugs do not crash the program immediately but cause instability or data corruption. You must still audit code logic carefully.
Misreading: Safe languages eliminate the need for dependency scanning
Correct reading: Safe languages often rely on large ecosystems of third-party libraries. These libraries introduce their own vulnerabilities. A memory-safe application can be compromised through a vulnerable dependency that handles network input. You must maintain a software bill of materials (SBOM) to track these components. Dependency updates are critical for maintaining security posture. Ignoring dependencies because the core language is safe is a dangerous oversight. Vulnerability scanning must include the entire dependency tree.
Misreading: Memory safety prevents all side-channel attacks
Correct reading: Side-channel attacks exploit physical implementations rather than code logic. Memory-safe languages do not inherently prevent timing attacks or cache-based leaks. An application can leak sensitive information through variations in execution time. Garbage collection pauses can create timing differences that reveal data. You must implement constant-time algorithms for cryptographic operations. You must manage cache usage carefully. Memory safety is orthogonal to side-channel resistance. Additional measures are required to mitigate these risks.
See also: Secure Software Development: Building Code That Resists Attack · Dependency Updates: A Step-by-Step Guide for Safe Rollouts
Misreading: Porting to a safe language fixes existing vulnerabilities
Correct reading: Porting code from an unsafe language to a safe language changes the memory model. It does not automatically fix logic errors or architectural flaws. Developers often port code line-by-line, preserving original design mistakes. The new code may still contain SQL injection or exposed admin panels. You must review the application architecture during the porting process. Do not assume the porting process cleans the codebase. Treat the port as a rewrite opportunity to improve security design.
Misreading: Safe languages are always more performant
Correct reading: Memory-safe languages often incur runtime overhead. Garbage collection pauses can affect latency. Ownership checks at compile time can increase compilation duration. This overhead is usually acceptable for most applications. It can be problematic for real-time systems or high-frequency trading. You must profile your application to understand the performance impact. Do not assume memory safety comes with zero cost. Balance security benefits against performance requirements.
Misreading: Memory safety eliminates the need for code reviews
Correct reading: Code reviews catch logic errors, poor design, and security policy violations. Memory safety catches memory errors. The two concerns are distinct. A code review can identify a missing authorization check that memory safety ignores. A code review can spot an insecure default configuration. You must continue regular code reviews. Relying on the compiler or runtime to catch all errors is insufficient. Human oversight remains necessary for complex security logic.
Misreading: Safe languages remove the need for penetration testing
Correct reading: Penetration testing evaluates the application from an attacker’s perspective. It finds logic flaws, configuration errors, and business logic vulnerabilities. Memory safety prevents only a subset of technical vulnerabilities. Penetration testing remains essential for validating security controls. You must test for SQL injection, command injection, and broken authentication. Memory safety does not replace manual security testing. Combine automated tools with manual assessment.
Misreading: All memory-safe languages provide the same guarantees
Correct reading: Different memory-safe languages use different mechanisms. Some use garbage collection, others use ownership types. These mechanisms have different trade-offs. Garbage collection can introduce non-deterministic pauses. Ownership types can make code harder to write and read. You must understand the specific guarantees of your chosen language. Do not assume all safe languages behave identically. Review the language documentation for security implications.
Misreading: Memory safety is a one-time fix
Correct reading: Memory safety is a property of the codebase and the language. It requires ongoing maintenance. New dependencies introduce new risks. New features introduce new logic errors. You must continuously monitor and update your application. Security is a process, not a product. Treat memory safety as one component of a broader security strategy. Include it in your regular development and operations workflows.
Misreading: Safe languages are immune to supply chain attacks
Correct reading: Supply chain attacks target the build process and dependencies. Memory-safe languages do not protect against malicious packages. An attacker can insert malicious code into a dependency. This code executes within your application. You must verify the integrity of all dependencies. Use signed packages and verified sources. Maintain a strict policy for introducing new dependencies. Memory safety does not protect the build pipeline.
Misreading: Memory safety eliminates the need for secure configuration
Correct reading: Configuration errors can expose sensitive data or functionality. Memory safety does not prevent misconfiguration. An improperly configured server can leak headers or allow unauthorized access. You must secure your deployment environment. Use least privilege principles. Encrypt sensitive data at rest and in transit. Memory safety is irrelevant if the configuration is broken. Secure the entire stack.
Misreading: Memory safety is only relevant for systems programming
Correct reading: Memory safety is relevant for all types of applications. Web applications, mobile apps, and desktop apps can benefit from memory safety. These applications often handle sensitive user data. They are frequent targets for attacks. Using memory-safe languages reduces the risk of memory corruption. It improves overall reliability. Do not limit memory safety to low-level systems code. Apply it across your technology stack.
Key takeaways
- Memory safety prevents invalid memory access but does not fix business logic errors or injection flaws.
- Safe languages shift risk from memory corruption to dependency management and supply chain integrity.
- Runtime overhead and garbage collection can introduce new availability risks and side-channel vectors.
Memory safety eliminates a specific class of vulnerabilities but does not replace comprehensive security practices. You must continue to validate inputs, manage dependencies, and secure configurations.
Frequently asked questions
Does using Rust or Go automatically secure my application?
No, these languages prevent memory errors but do not fix logic flaws, injection vulnerabilities, or configuration mistakes. You still need secure coding practices and regular security testing.
How do I handle dependencies in memory-safe languages?
Treat dependencies as critical components of your attack surface. Maintain a software bill of materials (SBOM) and apply dependency updates promptly to mitigate supply chain risks.
Can memory-safe languages still have performance issues?
Yes, garbage collection and runtime checks can introduce latency. Profile your application to ensure performance meets requirements, especially for real-time systems.
Is memory safety enough for compliance requirements?
No, most compliance frameworks require multiple security controls. Memory safety is one control. You must also implement access control, encryption, and audit logging.
How this guide was produced: written by the TechSec Feed editorial team with AI assistance, checked against the public references listed below, and reviewed when the facts change. See our editorial policy or report an error.